
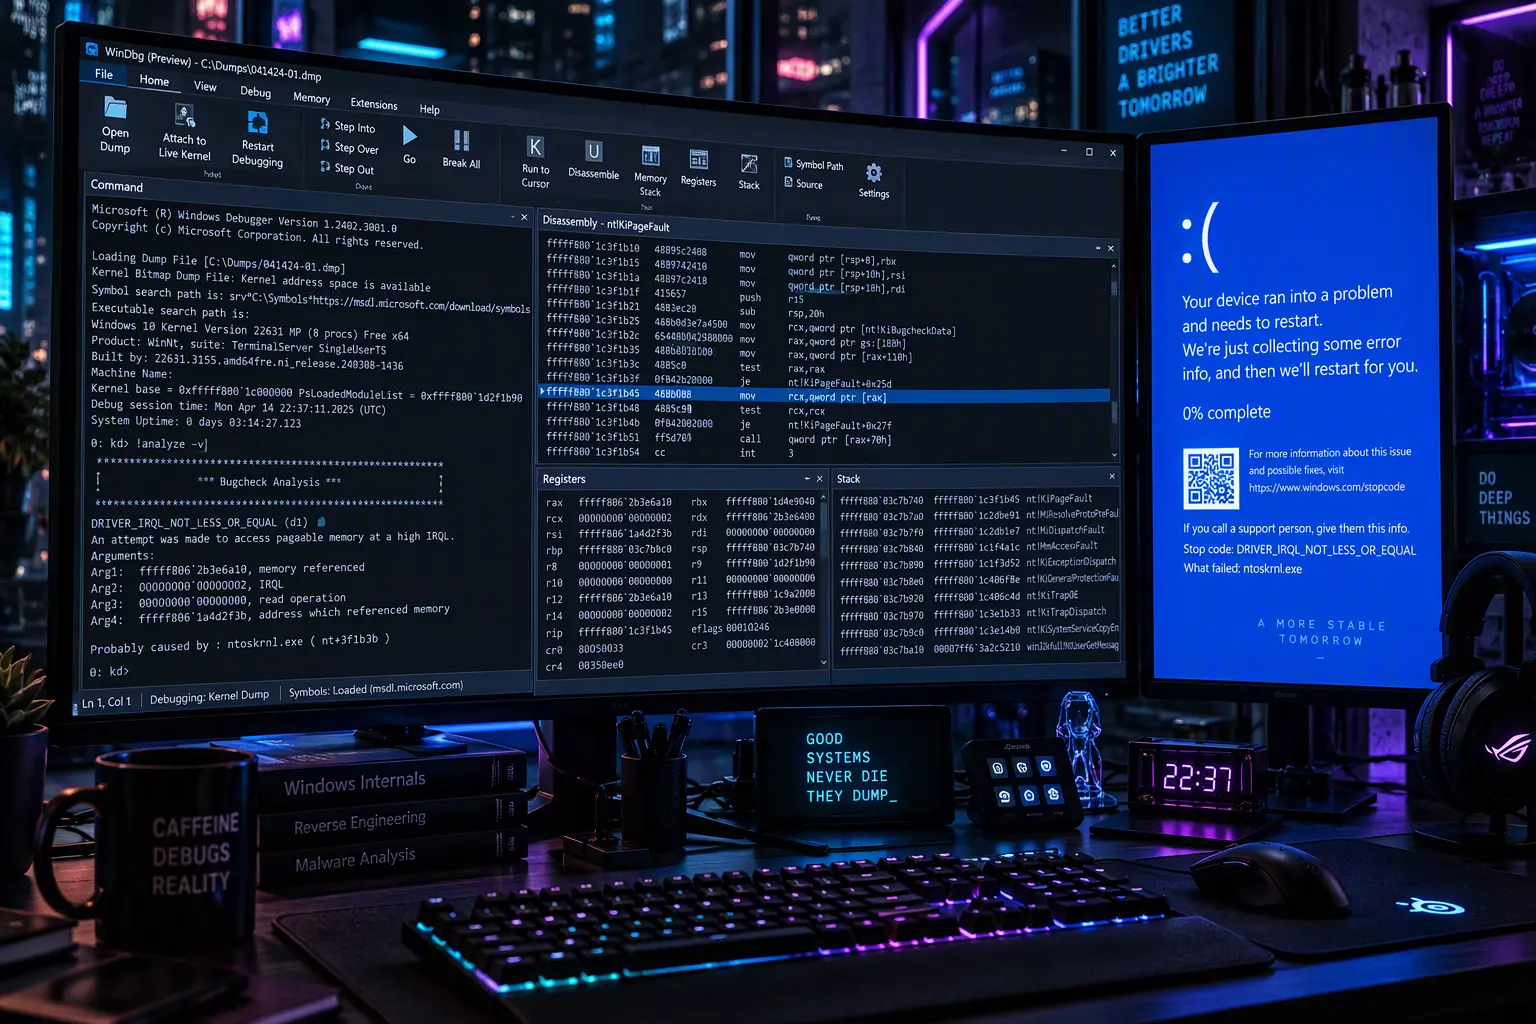
An unexpected Blue Screen of Death (BSOD) followed by a sudden reboot is one of the most frustrating issues encountered by system administrators and power users. Lightweight utilities like BlueScreenView often point blame at generic kernel binaries like ntoskrnl.exe or hal.dll, obscuring the genuine root cause. To accurately pinpoint the malfunctioning component, an engineer requires Microsoft’s professional kernel diagnostic suite: WinDbg (Windows Debugger). That is exactly why analyzing BSOD dumps via WinDbg is the gold standard for troubleshooting.
- Step 1. Configuring Windows for Minidump Retention
- Step 2. Installing WinDbg and Setting Up Symbol Servers
- Step 3. Analyzing BSOD via WinDbg: Running Heuristic Triage
- Step 4. Interpreting the Crash Report and Isolating the Culprit
- Step 5. Inspecting the Call Stack (STACK_TEXT)
- Frequently Asked Questions (FAQ)
Here is a step-by-step field workflow: configuring proper dump retention in Windows 11/10, loading official Microsoft debugging symbols, and tracking down the rogue .sys driver using automated heuristic triage.
Step 1. Configuring Windows for Minidump Retention
By default, Windows may attempt to write massive multi-gigabyte memory dumps or reboot without persisting diagnostic data. For driver localization, a compact Minidump (256 KB to 2 MB) contains all required telemetry.
- Press Win + R, type
sysdm.cpl, and hit Enter. - Navigate to the Advanced tab and click Settings under Startup and Recovery.
- In the Write debugging information drop-down menu, select Small memory dump (256 KB).
- Verify the dump directory path is set to
%SystemRoot%\Minidump(located atC:\Windows\Minidump). - Uncheck Automatically restart to ensure stop codes can be inspected visually.
| Dump Type | File Size | Captured Context | Best For |
|---|---|---|---|
| Small Dump (Minidump) | 256 KB – 2 MB | Stop code, call stack, loaded driver list, CPU registers | Rapid third-party driver triage |
| Kernel Memory Dump | 500 MB – 4 GB | Kernel-space memory only (omits user applications) | Complex hypervisor and OS subsystem errors |
| Complete Memory Dump | Equal to total RAM | Complete physical memory snapshot at time of crash | Deep hardware controller failure analysis |
Step 2. Installing WinDbg and Setting Up Symbol Servers
The modern Fluent UI-based WinDbg package provides seamless telemetry loading:
- Open the Microsoft Store, search for WinDbg, and click Install (or run
winget install Microsoft.WinDbgin PowerShell). - Launch WinDbg with Administrator privileges (mandatory for accessing protected directories inside
C:\Windows\Minidump). - To translate raw hex memory pointers into human-readable module and function names, configure the Microsoft Public Symbol Server. Navigate to File -> Settings -> Debugging settings and verify the Default Symbol Path:
srv*C:\Symbols*https://msdl.microsoft.com/download/symbols
Step 3. Analyzing BSOD via WinDbg: Running Heuristic Triage
Once a crash occurs, locate the newly generated .dmp file inside C:\Windows\Minidump:
- In WinDbg, go to File -> Open dump file (Ctrl + D) and select the target dump.
- The debugger initializes the session and automatically retrieves matching
.pdbsymbol files from Microsoft servers (status indicator in the command line will display BUSY). - Execute the automated triage extension by typing the following command and pressing Enter:
!analyze -v(Alternatively, click the blue inline
!analyze -vhyperlink in the initial output text).
Step 4. Interpreting the Crash Report and Isolating the Culprit
The !analyze -v command produces a comprehensive diagnostic dump. Focus on these critical telemetry fields:
- BUGCHECK_CODE: The hexadecimal stop code (e.g.,
0x0000000Afor IRQL_NOT_LESS_OR_EQUAL). - FAILURE_BUCKET_ID: The specific failure bucket signature used by Windows error telemetry.
- MODULE_NAME: The software or hardware module responsible for the violation (e.g.,
nvlddmkm,rtwlanu,vboxdrv). - IMAGE_NAME: The exact executable driver file name ending in
.sys.
To retrieve detailed binary properties (compiler build date, vendor signature, file version), run:
lmvm [driver_name_without_extension]Example: lmvm nvlddmkm outputs the exact NVIDIA GPU driver release date and file checksum.
Step 5. Inspecting the Call Stack (STACK_TEXT)
If IMAGE_NAME displays core kernel files such as ntkrnlmp.exe or ntoskrnl.exe, the kernel itself is almost never the actual root cause. The operating system simply trapped an invalid pointer passed by a third-party module.
In this scenario, scroll down to the STACK_TEXT block. Read the execution stack from the bottom upward: look for the last third-party driver module executed immediately before kernel trap functions like KeBugCheckEx or KiTrap0E. That driver is your actual culprit.
Frequently Asked Questions (FAQ)
Q: WinDbg throws an “Access Denied” error when opening the memory dump. What should I do?
A: The C:\Windows\Minidump folder is protected by system permissions. Copy the .dmp file to your Desktop or ensure you launch WinDbg with Administrator rights.
Q: Why does the analysis point to ntoskrnl.exe as the faulting module?
A: The Windows kernel is trapping a fatal memory exception. Carefully examine the call stack (STACK_TEXT) or check the thread stack with the kv command to identify the third-party driver that actually passed the bad memory pointer.
Q: Where are the debugging symbols cached locally?
A: Using the srv*C:\Symbols*https://msdl.microsoft.com/download/symbols string forces the debugger to download and store `.pdb` databases in the local C:\Symbols directory, significantly speeding up future analysis sessions.
Related Diagnostics Guides on SoftAndGadget:
- Network Diagnostics: Network & RDP Configuration Guides
- System Troubleshooting: Windows Error Resolution Directory
- System Software: Essential System Utilities Catalog
For homelabs, remote testing, and staging environments, we run NVMe VDS instances on Erahost. Fast provisioning, European routing, and predictable I/O.
View NVMe Plans →